Upcoming Events

NIH Bridge2AI Training WG Learning Module | Data Privacy and Federated Learning: Private Insights into GenAI Use by Dr. Peter Kairouz
October 8 @ 3:00 pm - 4:00 pm EDT
NIH Bridge2AI Training WG Learning Module | Data Privacy and Federated Learning: Private Insights into GenAI Use by Dr. Peter Kairouz
Scheduled: Oct 8, 2026 at 12:00 PM to 1:00 PM, Local Phoenix Time | https://arizona.zoom.us/j/86095514301
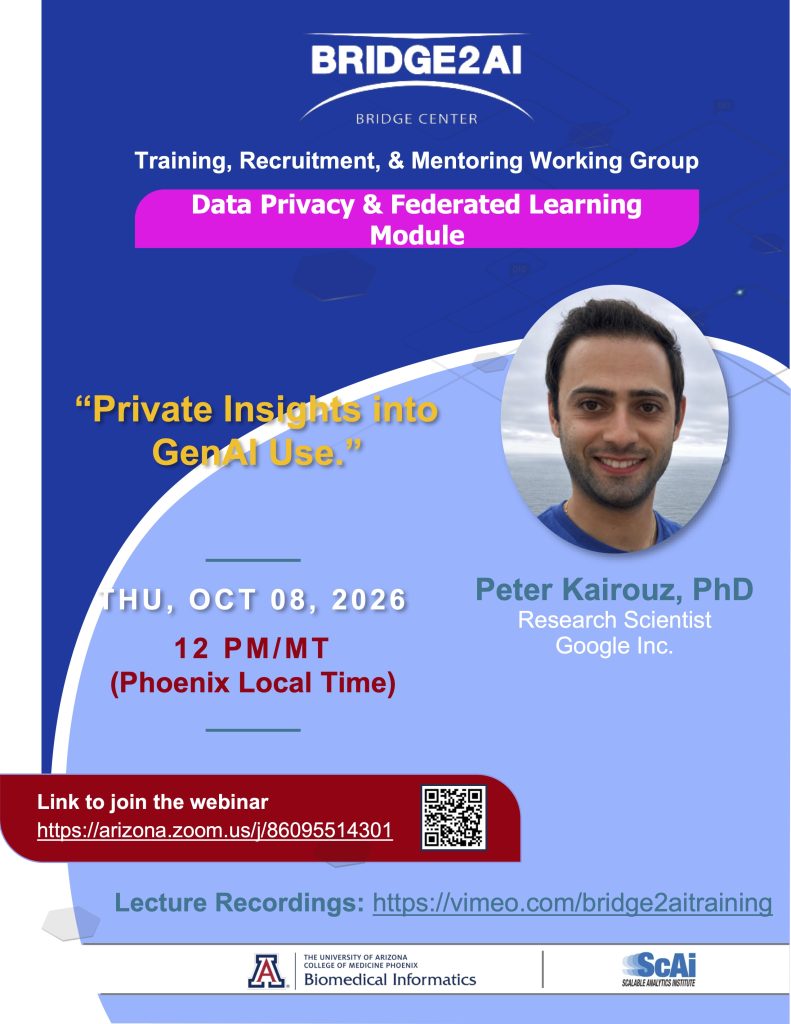
Dr. Peter Kairouz is a Research Scientist at Google, where he leads groundbreaking research initiatives focused on distributed, robust, and privacy-preserving machine learning. After earning his Ph.D. in Electrical and Computer Engineering from the University of Illinois at Urbana-Champaign and serving as a Postdoctoral Research Fellow at Stanford University’s Information Systems Laboratory, he has established himself as a significant voice on data privacy, differential privacy, and federated learning architecture. He is widely recognized for his foundational theoretical contributions, including defining optimal bounds for privacy loss under sequential execution via the composition theorem for differential privacy, and for co-authoring seminal field guides and reference frameworks like Advances and Open Problems in Federated Learning.
Continuing to push the boundaries of AI safety, Dr. Kairouz’s recent work investigates complex vulnerabilities in modern generative systems, such as context hijacking threats in conversational agents (highlighted by his pioneering work on AirGapAgent) and the systematic flaws of ad-hoc heuristics in GenAI analytics. By championing mathematically rigorous alternatives like Provably Private Insights, he bridges the critical gap between high-performance machine learning and uncompromised user data security at scale. An active leader in the research community, he has served as general chair for premier workshops on federated learning and analytics, and brings an extraordinary depth of vision to the future of trustworthy, decentralized AI ecosystems.
LEARNING OBJECTIVES
- Evaluate Heuristic Vulnerabilities: Analyze how ad-hoc, heuristic-based privacy protections (such as PII redaction and k-anonymity) fail against sophisticated data extraction methods like the CLIOPATRA attack.
- Understand Provably Private Frameworks: Examine the architecture and principles of Provably Private Insights (PPI) as a mathematically guaranteed alternative to heuristics for secure AI analytics.
- Explore Secure Deployment Technologies: Learn how integrating Trusted Execution Environments (TEEs), secure LLMs, and Differential Privacy enables scalable, privacy-preserving data extraction in real-world applications.